It’s that time of year again; when we look back at the improvements we’ve made to strengthen the Sentry System and ensure we’re delivering the best possible experience for our customers.

Over the past 12 months, our focus has been on enhancing security, streamlining workflows, and making it easier for users to manage their compliance responsibilities. Many of these updates have been driven by customer feedback, and we’d like to thank everyone who continues to share suggestions, ideas, and experiences with us. Your feedback plays a vital role in shaping the future of Sentry.

One of the most significant updates this year has been our continued investment in account security. Multi-Factor Authentication (MFA) is now automatically enabled by default when users log into Sentry, helping organisations strengthen protection against unauthorised access and cyber threats. As security expectations continue to evolve, we wanted to make it easier for customers to benefit from an additional layer of protection without requiring manual configuration. We’ve also simplified the login journey, with users now entering their email address or using Single Sign-On (SSO) before progressing to password entry, creating a cleaner and more intuitive sign-in experience.

We’ve made several improvements to reporting and visibility across the system. Breach exports now include staff members involved, alongside additional reporting fields, while Group Summary reports can now display restricted items where an administrator is the owner or an authorised member.

Our DPIA tools have received a range of enhancements, including the addition of review dates, reminder notifications for overdue reviews, improved exports, and clearer page titles to make navigation easier. Supplier management has also been strengthened with new supplier categorisation options, contract end date reminders, and updated guidance content.

For audits and compliance activities, we’ve introduced location checks, refreshed the audit templates, and added new Subject Access Request fields to help manage requests requiring clarification.

We’ve continued to refine the learning experience too. Test Results now display the answer selected by the learner, and course questions and answers have been reviewed to remove ambiguity. Updated help content across the Login, Settings, and Supplier areas also makes finding support quicker and easier.

Every enhancement we make is designed to help you get the most from Sentry while supporting your data protection and compliance responsibilities. Thank you for being part of our journey this year.

Let us know if you’d like support with any of these features, or if you have ideas for what we should tackle next. Here’s to another year of continuous improvement, collaboration, and helping you stay compliant with confidence.

The Sentry Team

If you’ve worked in education for any length of time, you’ve probably experienced the moment.

You’re halfway through a busy day. A colleague asks for some pupil information, a parent requests access to records, an email lands containing sensitive details, and somewhere in the background sits that annual data protection training that you vaguely remember completing a few months ago.

At times like these, data protection can feel like a separate discipline altogether. Something owned by compliance teams, policies, and legislation rather than classroom practitioners.

The reality, however, is quite different.

Every day, educators make decisions about personal information. Whether recording assessment outcomes, discussing safeguarding concerns, managing attendance, communicating with families, or sharing information with external agencies, data protection is woven into the daily life of schools.

The challenge is not learning a set of legal rules. The challenge is understanding how those rules help us make better professional decisions.

That’s where the seven data protection principles come in.

Rather than viewing them as legal requirements to memorise, it’s helpful to think of them as a framework for answering a simple question:

“Am I handling this person’s information in a way that is appropriate, respectful, and responsible?”

Let’s explore what that looks like in practice.


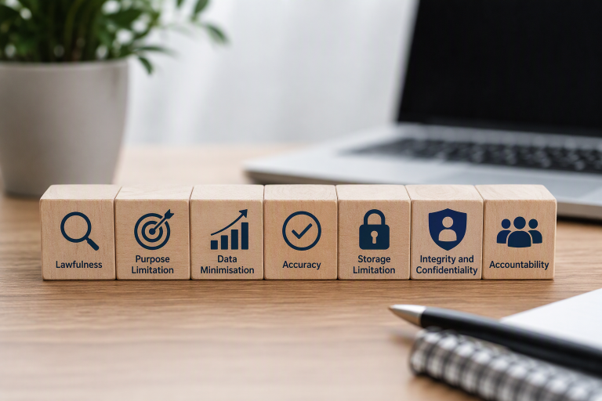
The Seven Data Protection Principles

Under UK GDPR, organisations must follow seven key principles:

  1. Lawfulness, Fairness and Transparency
  2. Purpose Limitation
  3. Data Minimisation
  4. Accuracy
  5. Storage Limitation
  6. Integrity and Confidentiality (Security)
  7. Accountability

On paper, they can appear abstract. In a school environment, however, they become much more tangible.


  1. Lawfulness, Fairness and Transparency

Let’s start with a familiar scenario.

A parent approaches reception and asks:

“What information does the school actually hold about my child, and why do you need it?”

Would the answer be clear and straightforward?

That’s the essence of this first principle.

Schools should be open about what information they collect, why they collect it, how it will be used, who it may be shared with, and how long it will be retained.

This isn’t simply about meeting legal requirements. It’s about building confidence.

When parents understand why information is needed, they’re more likely to trust that it is being used appropriately.

Educational organisations routinely explain the purpose behind their decisions, whether it’s a homework policy, a curriculum choice, or a behaviour strategy. Data protection is no different.

People deserve to understand what is happening with their information and why.


  1. Purpose Limitation

Imagine a member of staff develops a survey to understand pupil wellbeing.

The information gathered provides valuable insights, helps identify support needs, and informs pastoral interventions. Everyone agrees it was collected for a worthwhile purpose.

A few months later, someone suggests using the same data for an entirely different initiative.

At that point, it’s worth pausing.

The principle of purpose limitation reminds us that information should be collected for specific, legitimate reasons and not reused in ways that are incompatible with those original purposes.

In practical terms, schools should always be able to answer:

“Why are we collecting this information?”

For attendance data, the answer is usually obvious.

For safeguarding records, assessment information, medical needs, or parental contact details, the purpose is equally clear.

The difficulty often arises when collecting information simply because it might be useful one day.

Data protection encourages us to be more intentional than that.


  1. Data Minimisation

Education is a profession built on understanding people. Information helps schools and colleges identify patterns, recognise emerging needs, and make informed decisions that support learners. It’s therefore easy to see why organisations can sometimes be tempted to collect more data than they actually need.

But there is an important distinction between useful information and unnecessary information.

I once heard a school leader describe data minimisation as “the digital equivalent of packing for a weekend away.”

Most people intend to travel light.

Most people still arrive with three pairs of shoes, two coats, and a collection of items they never touch.

Schools can sometimes do the same with data.

A simple process gradually accumulates additional fields, additional forms, additional spreadsheets, and additional requests for information.

The principle of data minimisation encourages you to ask:

“Do we genuinely need this information to achieve our objective?”

If the answer is no, you should resist collecting it.

Collecting less information not only reduces risk but also makes systems easier to manage and maintain.


  1. Accuracy

Anyone who has ever entered data into a management information system knows how easily small errors can occur.

A mistyped phone number. An outdated address. A medical condition that has changed. A record that was accurate six months ago but no longer reflects reality.

Accuracy might sound like a technical requirement, but in education, it often has very human consequences.

Imagine trying to contact a parent during an emergency only to discover the details on file are wrong. Or imagine making a decision about pupil support based on outdated information.

Suddenly, accuracy becomes much more than a data quality issue. It becomes a safeguarding and wellbeing issue.

Good data protection reminds us that personal information should be reviewed regularly and corrected when necessary.

Reliable decisions depend on reliable information.


  1. Storage Limitation

Most schools have a cupboard, filing cabinet, or shared drive that contains resources nobody has looked at for years.

Some records remain because they are required; while others remain because nobody quite knows whether they can be deleted.

The storage limitation principle encourages schools to think more carefully. Information should not be retained indefinitely simply because storage space exists.

Instead, schools should understand:

  • Why information is being kept
  • How long it needs to be retained
  • When it should be securely disposed of

A helpful way of thinking about this is to imagine every record being accompanied by a small question:

“Do you still need me?”

If the answer is no, retention practices should ensure the information is appropriately removed.

Good record management is not about keeping everything. It’s about keeping what matters for as long as it matters.


  1. Integrity and Confidentiality (Security)

When people hear the phrase data breach, they often imagine a sophisticated cyberattack.

Certainly, cyber threats are real, and schools must take them seriously. Yet many data incidents arise from far simpler situations.

An email sent to the wrong recipient.

A confidential document left on a printer.

A discussion about sensitive information taking place where others can overhear.

A laptop left unlocked.

The reality is that information security is often less about technology and more about habits.

Every educator develops professional routines. We take registers, monitor safeguarding concerns, and adapt lessons based on pupil need.

Strong data protection requires similar routines:

  • Locking devices when unattended
  • Using strong passwords
  • Verifying recipients before sending information
  • Storing records securely
  • Sharing information on a need-to-know basis

These actions may seem small in isolation, but collectively they create a culture of security.


  1. Accountability

The final principle is perhaps the one that connects all the others.

Imagine an inspector, governor, parent, or regulator asks:

“How do you know your school handles personal information appropriately?”

Accountability means being able to answer that question with evidence.

Not simply saying:

“We take data protection seriously.”

But demonstrating it through:

  • Policies and procedures
  • Staff training
  • Privacy notices
  • Risk assessments
  • Governance arrangements
  • Incident reporting processes

For educators, this concept should feel familiar.

We’re accustomed to evidencing teaching, learning, assessment, and safeguarding practice.

Data protection follows the same logic. Good intentions are important, but evidence of good practice matters too.


The Principle Behind the Principles

Whenever data protection is discussed, conversations often drift towards compliance.

Policies. Audits. Forms. Training modules.

Necessary though these things are, they can sometimes distract from the bigger picture.

At its heart, data protection is about trust. Parents trust schools with sensitive information about their children. Pupils trust staff with personal concerns. Employees trust their organisations with professional and personal records.

Every decision about personal information either strengthens or weakens that trust.

Perhaps that’s why the seven principles remain so relevant. They’re not really about data. They’re about people.

They encourage us to pause before collecting information, sharing it, storing it, or disposing of it and ask:

“Am I handling this information with the same care and respect I would expect for my own?”

When educators adopt that mindset, the principles become less about compliance and more about professionalism.


The seven data protection principles are not isolated legal concepts to revisit once a year during mandatory training. They are practical guides that support everyday decision-making in schools.

By ensuring information is used lawfully and transparently, collected for clear purposes, limited to what is necessary, kept accurate, retained appropriately, secured effectively, and managed accountably, schools create environments where personal information is treated with the care it deserves.

And ultimately, that is what good data protection has always been about: not protecting data for its own sake but protecting the people behind it.
When conversations turn to data protection in schools and colleges, one word tends to appear more than any other: consent.

For many educators, consent can feel like the default answer to any question involving personal data. Yet one of the most surprising aspects of data protection law is that consent is often not the most appropriate basis for processing information.

Understanding when consent is necessary, when it is not, and when explicit consent is required can help schools make more confident decisions while maintaining trust with pupils, parents and staff.


Why Consent Isn’t Always the Answer

There’s a common assumption that if personal data is being used, consent must be obtained first.

In reality, schools process large amounts of personal information every day as part of their educational responsibilities. Attendance records, assessment data, safeguarding concerns and communications with parents are all examples of processing that is often necessary for a school to function effectively.

A helpful question to ask is:

If someone says no, can we genuinely stop processing their data?

If the answer is no, consent may not be the most appropriate lawful basis.

In these situations, relying on consent can create confusion because it suggests that individuals have a choice when, in practice, the processing still needs to occur.


When Consent Is Not Usually Appropriate

Attendance Monitoring

Schools have legal and safeguarding responsibilities to record attendance.

While pupils may not always be enthusiastic about having their attendance monitored, maintaining accurate attendance records is an essential part of a school’s role and does not depend on consent.

Safeguarding

Safeguarding is one of the clearest examples of processing that should not rely on consent.

If a member of staff has concerns about a child’s welfare, the school has a duty to act appropriately. In some circumstances, seeking consent before sharing information could delay important action or increase risk.

Recording Progress and Achievement

Assessment data forms the backbone of educational decision-making.

Whether recording test scores, tracking progress or reporting outcomes, schools need to process this information to support learning and meet their responsibilities.

Students may occasionally wish certain results could be quietly forgotten, but educational records remain an important part of supporting learning and development.

Essential Communications

Parents expect schools to communicate important information about their children and about school operations.

Messages regarding closures, timetable changes, behaviour concerns or academic progress are generally part of a school’s core responsibilities rather than activities requiring consent.


When Consent Is Appropriate

Consent works best when people have a genuine and meaningful choice.

Publicity and Promotional Activities

Many schools enjoy celebrating achievements through websites, prospectuses and social media.

Where participation is genuinely optional, consent can provide a clear and transparent way of giving individuals control over how their information is used.

Optional Photography

Photography often sits at the centre of data protection discussions in education.

Using a photograph internally for identification purposes may be very different from using it in promotional materials or on social media.

When images are being used beyond the school’s essential functions and individuals have a genuine choice, consent may be appropriate.

Alumni and Success Stories

Schools and colleges are rightly proud of their former students.

However, featuring a former pupil in a newsletter, website article or promotional campaign is very different from maintaining their educational record. In these circumstances, seeking consent is often the most respectful and transparent approach.


When Explicit Consent Is Required

Some situations require a higher standard than ordinary consent.

Explicit consent requires a clear and specific indication that the individual understands exactly what they are agreeing to.

This often becomes relevant when processing particularly sensitive information, including:

  • Health data
  • Biometric information used for identification
  • Religious beliefs
  • Ethnic origin
  • Certain other categories of sensitive personal data

Examples in education might include:

Sharing Personal Health Stories

A pupil may wish to participate in a fundraising campaign discussing their medical experiences.

While such stories can be powerful and inspiring, the use of detailed health information requires particularly careful consideration and may require explicit consent.

Publishing Sensitive Case Studies

A college may wish to highlight a student’s achievements while discussing challenges linked to a disability or health condition.

Because the information is sensitive, explicit consent helps ensure the individual understands and agrees to how that information will be used.


A Simple Consent Checklist

Before reaching for a consent form, consider:

  • Is there a genuine choice?
  • Could the individual refuse without disadvantage?
  • Can consent be withdrawn?
  • Is consent the most honest and transparent basis for the processing?

If the answer to any of these questions is unclear, it may be worth considering whether another lawful basis is more appropriate.


One of the most useful lessons data protection offers educators is that good practice is not about collecting the greatest number of consent forms.

Rather, it is about understanding why information is being used, being transparent about that use, and ensuring individuals’ rights are respected.

Consent remains an important part of the data protection toolkit, but it is only one tool among many. Sometimes the most responsible approach is not to ask for consent, but to identify the lawful basis that genuinely reflects why the processing is taking place.

As with good teaching, success often comes from asking the right question in the first place. In data protection, that question is not simply:

“Do we have consent?”

but rather:

“Is consent the right basis for what we’re doing?”

That’s where meaningful compliance begins.

Not so long ago, a teacher’s biggest technology concern was whether the interactive whiteboard would cooperate before Period 1. Today, we’re juggling AI-powered learning platforms, educational apps, social media, personalised learning algorithms, digital portfolios, and enough login credentials to make a cybersecurity expert break into a cold sweat.

It’s exciting. It’s innovative. It’s transformative.

It’s also a bit terrifying.

Because while we’re busy marvelling at how quickly AI can generate a quiz or differentiate a worksheet, a quieter question is lurking in the background:

At what point does a student stop being a learner and start becoming a dataset?


The Digital Gold Rush

Education technology has promised us many wonderful things. Greater accessibility. Personalised learning. Reduced workload. Better engagement. Faster feedback.

And to be fair, much of it delivers.

AI tools can support lesson planning. Learning platforms can identify gaps in understanding. Social media can connect classrooms with experts and opportunities around the world.

The challenge isn’t necessarily the technology itself. The challenge is that many of these tools are powered by one thing above all else: Data.

Every click, every search, every uploaded piece of work, every profile photo, every behaviour metric and every interaction potentially contributes to a growing digital footprint.

For adults, that’s a concern.

For children, it should be a priority.


The “But Everyone’s Doing It” Trap

We’ve all been there.

A colleague discovers a fantastic new AI tool. A tutorial appears on LinkedIn. An education influencer posts a glowing review on X. Suddenly; half the staffroom is experimenting with it before someone asks the awkward question:

“Where does the data actually go?”

Cue silence.

In education, enthusiasm often arrives before due diligence.

The pressure to innovate can sometimes make schools feel like participants in a giant educational technology experiment. Yet under UK data protection law, schools aren’t simply consumers of technology. They’re custodians of children’s personal information.

That distinction matters.

A lot.


Children Are Not Mini Adults

One of the most important principles in UK data protection is that children’s data requires particular care.

This is where things become especially significant for educators.

Adults often make informed decisions about sharing information online. We weigh risks and benefits. We understand, at least broadly, what we’re agreeing to.

Children don’t.

A Year 5 pupil uploading a piece of creative writing to an AI-powered platform isn’t making a data processing decision. They’re completing homework.

A Year 9 student appearing in a school social media video isn’t evaluating privacy implications. They’re participating in school life.

The responsibility sits firmly with us.


The Social Media Paradox

School social media accounts are a fascinating contradiction.

On one hand, they’re brilliant. They celebrate achievement, strengthen community relationships, showcase learning and provide a window into school life.

On the other hand, every photo, video and success story contributes to a permanent digital record.

The pupil proudly holding a certificate in Year 3 may not particularly appreciate that image resurfacing a decade later.

The child whose attendance at a particular school seems harmless to disclose today may have circumstances that make publicity less appropriate tomorrow.

None of this means schools should disappear from social media entirely. It simply means we need to move from asking:

“Wouldn’t this make a great post?” to: “Is this genuinely necessary, appropriate and proportionate?”

Those are surprisingly powerful questions.


When Westminster Starts Asking the Same Questions

Interestingly, schools are not the only institutions wrestling with these concerns.

Discussions about children’s use of social media have moved well beyond staffrooms and parent WhatsApp groups and into Parliament itself. From stronger age-verification measures and limits on harmful content to proposals for restricting social media access for under-16s, policymakers are increasingly questioning how digital platforms collect, use and influence children’s data and behaviour.

For schools, the detail of the legislation matters less than the direction of travel.

For years, the conversation was largely about getting children online and developing digital skills. Increasingly, the conversation is becoming:

How much access is appropriate, and at what cost?

That’s a significant shift.

And if Parliament is questioning how much information social media companies should hold about children, schools may find themselves asking similarly searching questions of ed-tech and AI providers.

Because from a pupil’s perspective, the distinction between a social media platform, a learning app and an AI-powered educational tool is often less obvious than it is to adults.

They’re simply digital environments collecting information about them.


AI Has Entered the Chat

Perhaps the most interesting challenge facing schools today is AI.

Generative AI has arrived with the enthusiasm of a supply teacher who thinks they’ve invented group work.

It’s everywhere.

Teachers are using it to create resources. Students are using it to support revision. Organisations are rapidly integrating AI into educational products.

Yet AI introduces an additional layer of complexity: data processing often becomes less transparent.

When information is entered into an AI system, educators need confidence about:

  • What data is being collected
  • Where it is stored
  • Whether it is used to train models
  • Who can access it
  • How long it is retained
  • Whether it leaves the UK

The reality is that many users never read the privacy information. And let’s be honest, some privacy notices appear to have been written specifically to discourage human consumption.

But schools cannot afford to rely on hope as a data protection strategy.

“Probably fine” is not a legal basis.


The New Digital Safeguarding

Traditionally, safeguarding discussions focused on physical safety and online behaviour. Increasingly, however, data protection is becoming a safeguarding issue in its own right.

A data breach doesn’t just involve information. It involves people.

Real children.

Real families.

Real consequences.

The accidental sharing of personal data, inappropriate use of AI tools, unsecured platforms or excessive data collection can create risks that extend far beyond compliance checklists.

In many ways, data protection and safeguarding have become close relatives. Different disciplines, perhaps, but increasingly dealing with overlapping concerns.

And as public awareness grows, schools should expect more questions from parents, governors and regulators:

  • Why does this platform need this information?
  • How long will it keep it?
  • Is student work being used to train AI models?
  • What happens to the data when a child leaves school?
  • Can information genuinely be deleted?

Not long ago, these were questions mostly reserved for Data Protection Officers.

Today, they’re becoming leadership questions.

They’re becoming governance questions.

And increasingly, they’re becoming safeguarding questions.


Building a Culture, Not a Checklist

The schools navigating this landscape most effectively aren’t necessarily the ones with the longest policies.

They’re the ones with the strongest culture.

A culture where staff regularly ask questions.

A culture where “free” software isn’t adopted without scrutiny.

A culture where privacy considerations are part of procurement conversations from the start.

A culture where children are taught not only how to use technology, but also how to understand the value of their own information.

In other words, a culture that treats data literacy as an essential life skill.

Because it is.


A Final Thought

The next generation will grow up in a world where AI is ordinary, social media is embedded into daily life, and digital identities are established long before adulthood.

As educators, we rightly spend enormous amounts of time helping young people protect their wellbeing, develop critical thinking skills and navigate online spaces safely.

Perhaps protecting their data deserves an equally prominent place on that list.

After all, a lost worksheet can be reprinted.

A forgotten password can be reset.

But once personal data enters the digital ecosystem, retrieving complete control over it becomes considerably more difficult.

And that may be the most important lesson technology is teaching us today.

The future of education isn’t just about teaching children how to use technology. It’s about ensuring technology uses children’s information responsibly in return.

Picture the scene: you’re juggling emails, safeguarding logs, and the eternal mystery of the staffroom milk, when someone appears at reception. It’s not Ofsted. It’s not a parent. It’s a police officer with a calm but direct request:

“We’d like to see the CCTV from Tuesday afternoon. Also, we need some information about one of your students.”

At that moment, your brain does a quick GDPR shuffle. Because as helpful as we all want to be when the police get in touch, you can’t simply hand over personal data and hope for the best.

You’re a data controller in a regulated environment, and every decision you make needs to balance cooperation with lawful, proportionate processing.


CCTV Footage: Press Play, With Care

Take a common example: there’s been an incident in the playground, and the police believe the CCTV might help with their investigation.

Reasonable? Yes. Automatic? No.

Always check the request is specific, proportionate, and targeted to the incident. Ideally, it should come with a formal written request and a defined time and location.

If the footage contains unrelated students or staff, redaction (such as blurring faces, cropping, or extracting only the relevant clip) should be considered. If redaction isn’t practical, you’ll need to weigh public interest against privacy rights and, if necessary, consult your Data Protection Officer (DPO).


Student Information: Proceed on a Solid Legal Basis

For personal details like a student’s home address, attendance records, or behaviour history, you must confirm a valid lawful basis before disclosure. Common examples include:

  • Legal obligation – where a statutory duty requires it.
  • Vital interests – where there’s a risk to life or serious harm.
  • Law enforcement purposes – typically for crime detection or prevention.
  • Recognised legitimate interests – a formal ground that can apply where sharing supports safeguarding or crime prevention, provided it’s necessary and proportionate.

Regardless of basis, ensure the request is relevant, proportionate, and justified. It’s fine to pause while you confirm details, request a formal form, or check with your DPO. This isn’t obstruction, it’s responsible compliance.


Redaction: Not Just for Government Files

Whether it’s a behaviour log, email exchange, or video clip, remove personal data not relevant to the investigation.

This is data minimisation in practice, sharing only what’s needed for the stated purpose. Other students’ or staff members’ details should be excluded unless their involvement is directly relevant.


Verification: Trust, But Verify

Uniforms don’t replace process. Before releasing data:

  • Confirm the officer’s identity.
  • Request a written, signed request.
  • Confirm the lawful basis for access.
  • Decide whether immediate disclosure is necessary or if a short delay is appropriate to clarify scope or seek advice.

Your role is not to default to “yes” or “no”. It’s to say “yes, where lawful and appropriate; no, where it’s not.”


Handling Requests Efficiently and Defensibly

Current standards also emphasise the importance of:

  • Keeping searches reasonable and proportionate – you are not obliged to trawl through every system if it’s not necessary.
  • Being able to pause the process while clarifying unclear or overly broad requests.
  • Maintaining clear, accessible channels for anyone to raise concerns about data handling and responding promptly and transparently.

These aren’t just compliance points. They also protect staff time, reduce errors, and ensure decisions are fully defensible.


Working with the police is an important part of keeping school communities safe. That cooperation must be balanced with the rights of individuals and the principles of lawful data handling.

When a request comes in:

  • Stay calm.
  • Clarify what’s needed.
  • Ensure a lawful basis.
  • Redact where necessary.
  • Document decisions.
  • Consult your DPO when in doubt.

Data protection isn’t about blocking cooperation. It’s about enabling it to happen the right way, every time.

Walk into any staffroom and you’ll find no shortage of conversations about pupils, lesson planning, or whether the photocopier is plotting against humanity. But lately, one topic has been surfacing with a frequency that rivals debates over whose turn it is to make tea: data sharing.

A teacher might quietly lean over and ask, “Can we just give this information to the exam board?” The question hangs in the air like an awkward silence at parents’ evening. The hesitation isn’t about whether exam boards, local authorities, or software providers need data. It’s about whether schools are allowed to share it, and under what rules.


Can schools share data with exam boards, local authorities, or software providers?

The answer is: yes, but not without conditions.

  • Exam Boards: Sharing is expected, even essential. Students can’t get their qualifications without their information being passed on.
  • Local Authorities: Again, lawful grounds are clear. Safeguarding, funding, statutory reporting – these all require cooperation.
  • Educational Software Providers: This is where the situation becomes less straightforward. The promise of personalised dashboards and data-driven insights is appealing, but schools are essentially opening the door to a third party. And opening that door means asking, “What safeguards are in place?”


Enter the Agreement Stage

Before any student data travels beyond school walls, an agreement must spell out the terms. This is where the much-referenced Data Processing Agreement (DPA) comes into play.

Think of it as the rulebook for handling your most valuable assets. A DPA is not just bureaucratic red tape. It’s the backbone of responsible data sharing.

Here’s why it matters so much:

  1. Clarity of Roles: A DPA defines who is the data controller (usually the school) and who is the data processor (the provider). Without this clarity, accountability quickly gets lost in the shuffle.
  2. Boundaries of Use: It locks down the purpose of processing. If you share attendance data with a software provider, the DPA ensures they use it to track attendance; not to build a new marketing tool or sell analytics elsewhere.
  3. Security Commitments: The agreement creates an obligation for the third party to protect the data. Whether that means encryption, access controls, or safe storage. No one wants student records floating around on an unprotected server.
  4. Deletion and Retention: Data isn’t supposed to live forever. A DPA makes clear when and how information will be deleted once it’s no longer needed.
  5. Legal Protection: If something goes wrong (and in the digital world, something will go wrong at some point), the DPA is evidence that the school did its due diligence. It demonstrates compliance with data protection law, and that can make the difference between a slap on the wrist and a full-blown investigation.

Without a DPA or a similarly robust contract, sharing data with third parties is a bit like giving a stranger your house keys and trusting them not to copy them. It might work out fine, but it’s not exactly wise.


The Bigger Question

What makes this debate more than just “admin” is the realisation that data isn’t simply numbers on a spreadsheet. It’s the narrative of a young person. Their achievements, struggles, and growth. When schools share it, they’re sharing that story with someone else. And with that comes a responsibility: to ensure the recipient is trustworthy, transparent, and bound by rules that protect the child behind the data.

Data sharing, when done correctly, enables collaboration, efficiency, and innovation. But it’s never as simple as “yes” or “no.” It’s always “yes, and here are the safeguards we insist on.”

Perhaps the paperwork feels heavy at times, but like seatbelts, it’s there for good reason. To protect everyone on the journey.

If you’ve ever hesitated before hitting “send” on an email about a student concern, you’re not alone. For educators, the tension between safeguarding responsibilities and privacy rights, especially under GDPR, is a daily challenge. We want to protect our pupils, but we also need to protect their personal data. So how do we walk that line without falling off either side?

Let’s start with two real-life scenarios.


Case Study 1: Sharing Too Much

A primary school teacher became concerned when a pupil started showing signs of anxiety and withdrawing from classroom activities. Wanting support, the teacher emailed a wide group of colleagues with a detailed account of the pupil’s behaviour and personal circumstances.

Although the intention was to help, the level and breadth of information shared went beyond what was necessary. Under UK GDPR, personal information should only be shared with staff who genuinely need it in order to provide support. In this situation, the message reached colleagues who were not directly involved, leading to an avoidable breach of the pupil’s privacy.
The school’s Data Protection Officer later offered guidance, reminding staff that safeguarding is important, but it does not justify unrestricted or overly broad information sharing.


Case Study 2: Sharing Too Little

In another school, a member of staff overheard a student making worrying comments about self-harm. Unsure whether the concern was serious, and worried about “getting it wrong” or mishandling confidential information, the staff member chose not to pass the concern on.

Later, the student required significant support, and it became clear that earlier reporting could have enabled help to be put in place much sooner. The staff member had misunderstood data protection laws, thinking they prevented sharing.
In fact, UK GDPR explicitly allows the sharing of personal data when it is necessary to safeguard a child or protect their wellbeing. In this scenario, not reporting the concern carried a much greater risk than sharing it appropriately.


GDPR: What Educators Need to Know

Under the UK General Data Protection Regulation (GDPR), schools are considered data controllers. That means they must ensure personal data is:

  • Processed lawfully, fairly, and transparently
  • Collected for specified, explicit purposes
  • Limited to what is necessary
  • Kept accurate and up to date
  • Stored securely

But GDPR also makes clear that safeguarding trumps privacy when a child is at risk. The key is proportionality, sharing the right information with the right people at the right time.


How Data Protection and Safeguarding Duties Work Together

It’s easy to think of GDPR and safeguarding as being in conflict, but in reality they are designed to complement each other. Safeguarding duties set out in statutory guidance, such as Keeping Children Safe in Education (KCSIE), require schools to act swiftly when a child may be at risk. Data protection laws don’t override those responsibilities; instead, they help ensure that any information shared during safeguarding processes is handled appropriately.

Under UK GDPR, schools must identify a lawful basis for sharing personal data. In safeguarding contexts, this is often “public task” or “vital interests,” both of which allow information to be shared without consent when necessary to protect a child. The law recognises that waiting for consent could introduce delay and increase risk.

At the same time, GDPR emphasises proportionality. Only the minimum relevant information should be shared – enough for the DSL, external agencies, or other professionals to act effectively, but no more than is necessary. This principle ensures that children’s privacy is still respected even in urgent or high‑risk situations.

Rather than opposing forces, GDPR and safeguarding should be seen as working in partnership: one focused on preventing harm, the other on preventing unnecessary exposure of personal information. Used together, they support safer, more responsible practice across schools.


Practical Tips

  1. Know your safeguarding lead
    Always report concerns through your Designated Safeguarding Lead (DSL). They’re trained to assess risk and determine what information needs to be shared, and with whom.
  2. Use secure systems
    Avoid casual emails or verbal disclosures. Use your school’s safeguarding platform or secure reporting tools to log concerns.
  3. Keep it factual
    Record what you saw, heard, or were told without speculation. Stick to objective observations.
  4. Ask yourself: is this necessary?
    Before sharing, consider whether the recipient needs the information to act in the child’s best interests.
  5. Don’t let GDPR paralyse you
    GDPR is not a barrier to safeguarding, it’s a framework to ensure data is handled responsibly. If a child is at risk, you are legally and ethically obliged to act.


Balancing safeguarding and privacy isn’t easy but it’s essential. GDPR doesn’t ask us to choose between protecting children and protecting data. It asks us to do both, thoughtfully and responsibly.

So next time you’re unsure, remember safeguarding is a lawful basis for sharing data. But share just enough, with just the right people, and always with the child’s best interests at heart.

It’s a Tuesday morning and the Year 8 maths teacher bursts into the staffroom, laptop clutched to her chest.
“I think I’ve just emailed the wrong attachment to a parent,” she says, eyes wide.

For most people outside education, this might sound like a small blip. But for those working in schools, it’s the sort of stomach-dropping moment that makes your mind race: What was in the attachment? Who has it now? Is this serious enough to tell the ICO?

Schools hold a vast amount of personal information; names, addresses, contact details, attendance, health data, safeguarding records, and that makes them particularly vulnerable to data breaches. And while many incidents are small and easily contained, others need urgent reporting to the Information Commissioner’s Office. The challenge is knowing the difference.


Step 1: Understanding the data involved

The first question to ask is deceptively simple: what kind of data are we dealing with?
Some breaches involve ordinary personal data like names, class lists or email addresses which, while still important, generally pose less risk. Others involve special category data, which is far more sensitive: health information, details of a child’s learning needs, or safeguarding reports.

Imagine a staff member sends an after-school club schedule to parents but accidentally leaves all the parent email addresses visible. Annoying, yes, but unlikely to cause real harm. Compare that to the SEN register being emailed to the wrong organisation, revealing medical diagnoses and support plans for vulnerable pupils. The stakes are suddenly much higher.


Step 2: Thinking about the potential harm

The severity of a breach isn’t just about what data is involved, it’s also about what could happen as a result. Could the information be used to cause embarrassment, distress, discrimination, or even physical harm? Does it involve a vulnerable individual, like a child under safeguarding measures?

A staff meeting agenda posted in the wrong place might cause mild irritation. But a safeguarding referral accidentally sent to multiple parents? That’s a different matter entirely as the potential for harm is clear and significant.


Step 3: Considering scale and exposure

One child’s name sent to the wrong person may still be a breach, but the risks are magnified when the same error involves dozens of pupils or is shared beyond the school’s control. And it’s not always digital slip-ups we need to worry about.

Take the example of a lost unencrypted USB stick containing last term’s exam results. If it’s dropped somewhere in the school car park and quickly recovered, the risk may be minimal. But if it goes missing on the bus home and could be accessed by anyone, the potential for wider exposure grows, and so does the severity.


Step 4: Deciding whether to contact the ICO

The ICO must be informed within 72 hours if a breach is likely to put someone’s rights or freedoms at risk. That’s a deliberately broad test, because context matters.

If the breach involves non-sensitive data, was quickly contained, and presents no realistic risk of harm, you might decide that ICO notification isn’t necessary. Though you should still keep a detailed internal record. But if the breach involves sensitive data, a vulnerable person, or uncontrolled exposure, the safer route is to report it.

Picture two incidents happening on the same day:

  • In the first, a parent receives the Year 9 timetable in error, showing pupil names and subjects. They tell the school immediately, delete the file, and confirm it’s gone. Annoying, but low risk.
  • In the second, an educational psychologist’s report containing detailed mental health notes for a pupil is emailed to the wrong parent. Sensitive data, real potential for distress, and no certainty it will be deleted. This needs reporting, and quickly.


When a breach happens in a school, the instinct is often to fix it quietly and move on. But the law, and more importantly the duty of care to pupils and families, means you can’t afford to guess.

Assess the nature of the data, the potential for harm, the scale of the exposure, and the likelihood that harm could occur. Then decide whether the ICO needs to know, and if you’re unsure, err on the side of caution.

Because at the heart of every spreadsheet, email, and USB stick is a child or family who trusts you to keep their information safe. And that trust is worth protecting above all else.

We’ve Rebranded! Introducing the New Look of GDPR Sentry.

We’re excited to unveil the refreshed brand identity of GDPR Sentry, including our new logo, designed to reflect our commitment to clarity, trust, and uncompromising data protection.

While our look has evolved, our purpose remains the same: helping schools, trusts, and education providers stay compliant, confident, and fully supported in every aspect of GDPR. This re‑brand marks an important step forward as we continue developing solutions that simplify data privacy and strengthen your compliance journey.

Thank you for trusting GDPR Sentry to safeguard what matters most.

Let’s be honest: GDPR isn’t the most thrilling part of your job. It’s not going to earn you a gold star or a round of applause in the staffroom. But it will keep your school safe, your students protected, and your inbox free from the dreaded “URGENT: Possible Data Breach” email.

So if you’re an educator juggling lesson plans, safeguarding concerns, and the occasional coffee spill, here’s your friendly reminder that data protection is a daily habit, not a once-a-year training module.

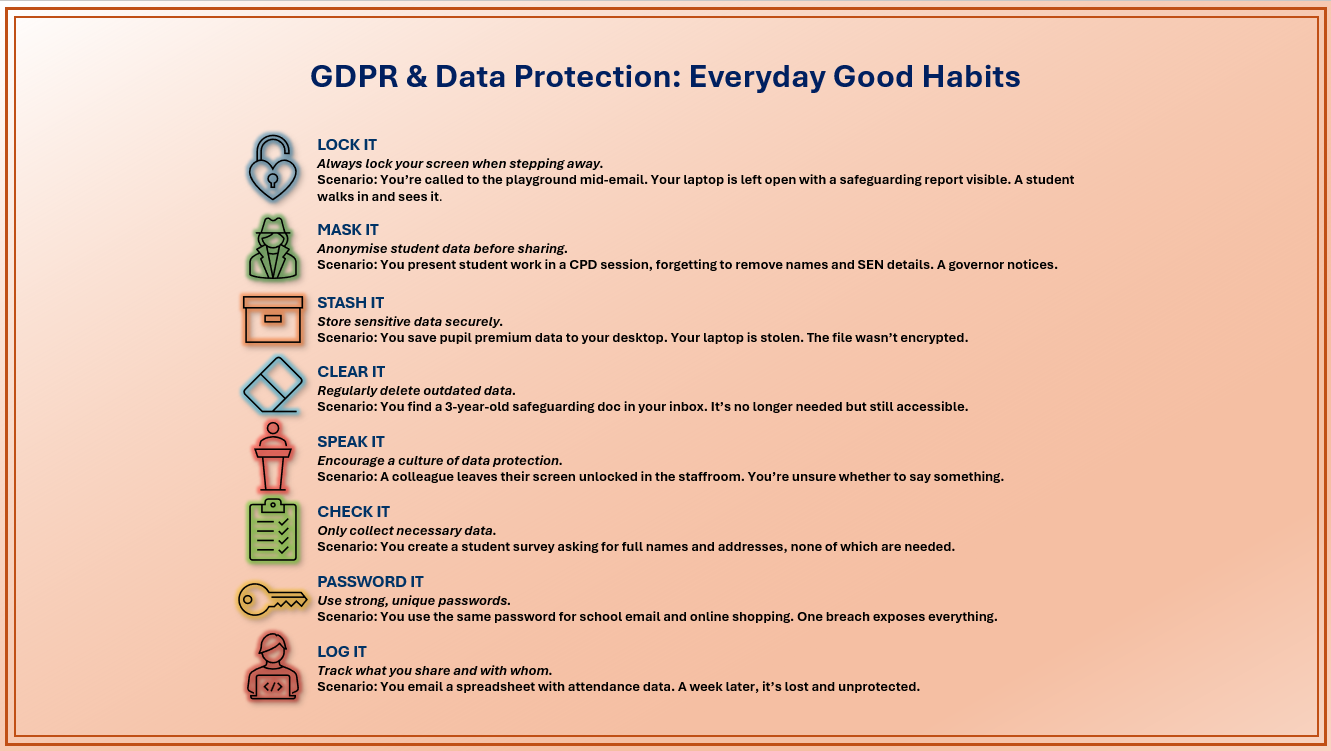
Let’s revisit our trusty trio – Lock it, Mask it, Stash it, and add a few more good habits.

Lock It – Because Screens Don’t Need an Audience

Scenario:
You’re called out of your classroom to deal with a playground incident. In your rush, you leave your laptop open on your desk with a safeguarding report on the screen. A curious student wanders in and sees more than they should. Later, they mention it to a friend, and suddenly sensitive information is circulating.

Good habit:
Hit Windows + L or Ctrl + Command + Q on a Mac every time you step away. Set your device to auto-lock after a few minutes. It’s like closing the door on sensitive data.


Mask It – Anonymise Like You’re in a Spy Movie

Scenario:
You’re leading a CPD session and want to showcase a brilliant piece of student work. You project it on the screen… and realise too late that it includes the student’s full name, class, and SEN status. A visiting governor notices and raises concerns.

Good habit:
Before sharing, ask: “Could someone identify this student?” If yes, anonymise. Use initials, remove photos, blur names. Think MI6, but with worksheets.


Stash It – Store Smart, Not Just Somewhere

Scenario:
You save a spreadsheet of pupil premium data to your desktop “just for now.” Weeks later, your laptop is stolen from your car. The file wasn’t encrypted. Cue panic, paperwork, and a very uncomfortable conversation with leadership.

Good habit:
Use school-approved cloud storage. Encrypt sensitive files. Never store personal data on USB sticks unless they’re encrypted and never leave them in your coat pocket.


Clear It – Declutter Your Digital Life

Scenario:
You search your inbox for a parent’s email and stumble across a safeguarding document from three years ago. You don’t need it anymore, but it’s still sitting there, vulnerable. If your account were compromised, that data could be exposed.

Good habit:
Schedule a monthly “data declutter.” Delete what’s outdated, archive what’s essential. GDPR loves a tidy inbox.


Speak It – Make Data Protection a Team Sport

Scenario:
You notice a colleague leaving their screen unlocked in the staffroom while they grab a coffee. You hesitate to say anything… but what if a student walks in? Or a visitor?

Good habit:
Speak up. Start a “Data Protection Minute” in staff meetings. Share one tip, once a month. It’s painless, and it builds a culture of care.


Check It – Know What You’re Collecting (and Why)

Scenario:
You create a Google Form to collect feedback from students. You ask for full names, dates of birth, and home addresses (none of which are actually needed). A parent complains after seeing the form.

Good habit:
Stick to data minimisation. Only collect what’s necessary. If you don’t need it, don’t ask for it. Less data = less risk.


Password It – Strong, Unique, and Not “Password123”

Scenario:
You use the same password for your school email, your personal Netflix account, and your online shopping. One breach, and everything’s exposed. Worse, your school account is used to send phishing emails to parents.

Good habit:
Use a password manager. Enable two-factor authentication. And never write your password on a sticky note stuck to your monitor (yes, we’ve all seen it).


Log It – Keep Track of What You Share

Scenario:
You email a spreadsheet to a colleague containing student attendance data. A week later, they can’t find it, and you’re unsure who else might have access. You didn’t password-protect it, and now it’s floating around inboxes.

Good habit:
Keep a simple log of what you’ve shared, with whom, and when. Use password protection for sensitive documents and send passwords separately.


You don’t need to be a tech wizard or a GDPR guru. You just need to be mindful, and act. Every locked screen, anonymised document, and securely stored file is a step toward a safer, smarter school.

So next time you’re tempted to save something “just for now” or leave your laptop unattended, remember: Lock it. Mask it. Stash it. Clear it. Speak it. Check it. Password it. Log it.

Your students deserve it. Your school depends on it. And your future self will thank you.